
JML Lifecycle: Key Steps for Proper Access Management
The joiner-mover-leaver (JML) lifecycle is the process of managing access when someone joins the company, changes roles, or leaves. It sounds simple, but in reality, it comes with several challenges.
Many IT teams deal with outdated data, slow ticket handoffs, and disconnected systems that affect JML processes.
For example, a new hire may need five apps on day one, yet hiring managers fail to communicate this important detail. Role changes can also be missed or logged late, which leaves old access active.
Offboarding is just as hard when people leave fast, use shared accounts, or still have lingering access to sensitive data.
This guide breaks down the key steps involved for each JML lifecycle stage: joiners, movers, and leavers. You’ll learn what to set up first, what to review later, and what to automate so you cut manual work.
TL;DR
- The JML lifecycle provides clear steps to manage access for joiners, movers, and leavers from start to exit.
- For joiners, you need to create digital identities, prepare devices and accounts before day one, assign role-based groups, and provision access to necessary tools.
- To manage movers, track user changes in real time, match new roles, revoke old access, and add only what fits the new job.
- When dealing with leavers, deactivate their accounts first before removing access, moving data, reclaiming assets, and confirming the exit.
- ezOnboard helps you manage joiners, movers, and leavers without extra effort.
What Is the JML Lifecycle?
The JML lifecycle is a framework in identity and access management (IAM) that governs user identities and access rights throughout an employee’s time at an organization.
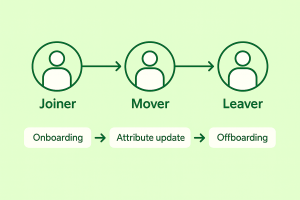
It tracks how access changes in three key stages: joiner, mover, and leaver. The goal is to make sure the right people have access to the necessary tools at the right time.
For IT teams, effective JML lifecycle management matters because it keeps access aligned with role changes and job requirements.
This helps maintain security, protect sensitive data, improve audit readiness, and avoid compliance failures. It also supports smoother onboarding, proactive change management, and faster offboarding.
JML Lifecycle Key Stages and Steps
The JML lifecycle is divided into three stages. Each phase requires clear steps to ensure appropriate access rights, from day one through exit.
Joiners
Joiners are new hires, interns, or contractors who need access to accounts and tools required for their jobs.
During this onboarding stage, you need to set up new employees quickly and securely. The goal is to accelerate time-to-productivity without sacrificing security and regulatory compliance.
Here’s the step-by-step process of managing joiners in your organization.

Step #1: Identity Creation
Start the joiner stage by creating digital identities in your main directory service. Connect it to your HR tech stack and make it the trigger. This makes sure every hire gets a record that matches their name, start date, manager, and department as soon as they join your company.
Create a unique user ID and a primary email address. Next, set up single sign-on (SSO) and multi-factor authentication (MFA) rules from day one using an identity provider system.
Then, match the digital identity to a worker type (full-time, contractor, intern) so access policies apply correctly.
Don’t forget to log the creation event so you can trace who created the user account, when, and from which HR record.
Step #2: Preboarding
Preboarding sets new employees up before day one so they can start work immediately without needing access requests.
During employee preboarding, build a starter package for each department that includes email, chat, and other core systems. Assign it as soon as HR confirms the new employee.
IT managers should also order the right devices, install the necessary software licenses, prepare the new employee’s desk, or coordinate equipment delivery if welcoming a remote hire.
Step #3: Role and Group Assignment
Once you’ve created digital identities and completed preboarding, assign the new hires to standard roles and groups.
Create role templates for teams, such as human resources, finance, and marketing. Each template should link to approved groups in SSO, cloud services, and SaaS management software.
Avoid one-off group adds unless there is a clear business need. If an exception is required, record who approved it and set a review date.
Effective role mapping keeps employee access tied to actual job functions.
Step #4: User Provisioning
Provisioning is the process of granting access permissions to devices, software licenses, company data, and other organizational resources.
To do this successfully, connect your identity governance and administration (IGA) tools to IT management SaaS software. This integration automatically triggers account creation and access provisioning based on predetermined rules.
It reduces onboarding tickets, which enables IT teams to focus on business-critical projects rather than repetitive tasks.
Step #5: Verification and Access Reviews
After provisioning, confirm the user has the right access based on their job title or function, and nothing more.
Then, compare their access privileges to your role templates. Birthright access helps speed up onboarding, but it can also introduce security risks if the default set is too wide.
To prevent that, always review required access with the manager and direct supervisor within the first week. Revoke permissions that don’t match the role.
Movers
Movers are employees who change roles, teams, or duties within your organization. This stage of the JML lifecycle is where access often drifts, because people gain new user permissions but keep old ones.
As an IT manager, it’s your job to adjust access so it matches the new role and close security gaps. Below are the key steps to follow:
Step #1: Internal Transfer Monitoring
Set up proactive alerts for role changes. Your HR system should be the main trigger, but don’t rely on it alone. Sometimes, human resources staff may forget to update the user’s role in their system.
Build a simple feed from workforce identity platforms, IT service management (ITSM) tickets, and manager notices. Then, use it to track employee lifecycle events in real time.
Step #2: New Role and Entitlement Mapping
Once you know a move is happening within your company, map the person to a new role template. Use the same access library you built for joiners to keep access management clean.
It’s important to review what the new user needs in each app and system.
If roles are complex, consider using attribute-based access control (ABAC) to grant access based on the user’s department, job level, or location.
For example, you will only grant access to sensitive financial data if the individual meets the required department in “finance,” has a “manager” position, and is located in the “United States.”
Step #3: Risk-based Access Approval
Not all access needs the same level of review.
Low-risk apps can follow auto-approval workflows tied to role-based access controls (RBAC). However, critical systems require additional checks and clear sign-offs.
Route access requests to the employee’s direct supervisor first, then the IT team. Keep approvals in one system so you can audit later.
Step #4: Removal of Legacy Access Rights
Before adding new access, remove what no longer fits the role. This is where most IT departments fall short.
First, identify the user’s old groups, app roles, and licenses, then compare them to the new template. Remove anything that’s not on the new list unless there is a clear time-boxed reason to keep it.
If you allow temporary overlap, set an auto-expiration date to avoid privilege creep that may potentially lead to security breaches.
Prioritize revoking access to sensitive systems, shared drives, collaboration tools, and cloud services first before moving on to other low-risk apps.
Step #5: Provisioning of New Access
After cleanup, add the new access tied to the mover’s role, department, and location. Automate provisioning through SSO or IGA platforms to save time and reduce security risks.
If a mover needs extra access outside the template, tag it as an exception and attach the approval. These access adjustments should be rare, time-bound when possible, and reviewed later so they don’t become permanent drift.
Step #6: Post-Move Access Recertification
You should immediately review and validate user access rights as soon as the user changes roles, moves departments, or gets promoted.
Look for two things: any tools they no longer need from the old role, and any gaps that slow down their new work.
Remove access to apps that no longer fit the new job and disable accounts that were only meant to help during the handoff.
End the process with a quick sign-off from the manager or app owner. Don’t forget to log what you changed to make sure you have a clear record later.
Leavers
Leavers refer to people who exit the company, whether by resignation, contract end, or termination.
During this offboarding stage, you should remove access fast, recover IT assets, and leave a clear record of what happened.
This reduces the business risk of lingering access in orphaned accounts and helps you maintain a strong security posture.
Let’s break down the steps involved in the leaver process:
Step #1: Offboarding Event Trigger
Use HR systems as the main source of termination events. Set your user access management tools to monitor any status change to “terminated” or “inactive” in your HR software. That way, the offboarding process starts the same minute HR employees log it.
That said, don’t depend on HR alone. Let managers and direct supervisors flag urgent exits in your ticket system, especially for same-day terminations.
Build a simple “urgent-exit” form with required fields: user ID, last working hour, manager name, and reason type. Route that form to both IT and security teams with a high-priority tag.
Step #2: Account Deactivation
After learning about the user’s departure, you can disable accounts.
Deactivate mailboxes, VPNs, and communication tools. Then, end active sessions to make sure former employees can’t stay logged in on a laptop or phone.
Check shared accounts they may know and change passwords right away. This step is the fastest way to remove access before you clean up everything else.
Step #3: Access Revocation and Deprovisioning
Remove access in every app and system that the departing user touched. Start with admin rights and privileged accounts.
Next, revoke permissions in tools that handle sensitive information, such as payroll, HR information system (HRIS), and customer records.
Then, move through the rest of your apps, one by one, using a standard offboarding checklist. Don’t forget shared drives, team spaces, and any tools the person used for past projects.
Consider automating user deprovisioning to make sure access is automatically revoked as soon as HR confirms an individual’s exit.
Step #4: Data Ownership Transfer
Before deleting accounts permanently, make sure to transfer important data to the right people.
Ask the manager to name a new owner for shared folders, dashboards, repos, and service accounts. Transfer file and cloud resource ownership, not just access.
Keep data retention rules in mind so you don’t lose records needed for legal, compliance, or business reasons. Make a short list of what was transferred and to whom, then attach it to the leaver or offboarding ticket.
Step #5: Hardware and Software License Reclamation
Once you’ve transferred important files, you can safely recover IT assets.
Collect laptops, phones, badges, and any other gear tied to the leaver. If they work remotely, send return labels, share shipping instructions, and provide a clear deadline.
Lock the hardware device after the last workday, then wipe data after checking in. Reclaim software licenses after the data handoff is done, so teams don’t lose access to shared work.
Doing both reduces risk and costs tied to hardware and software.
Step #6: Audit Trail Generation
Create a clean record of every action throughout the entire identity lifecycle. Log when the offboarding trigger came in, when accounts were disabled, which apps were removed, and who approved any exceptions.
Save reports from all systems (identity lifecycle management platforms, ticketing tools, HR software) in one place.
Accurate logs help you identify gaps and support compliance audits. If a third-party firm asks why access was removed, you can point to the ticket history.
Complete records are also useful during security reviews tied to data breaches or exit disputes.
Step #7: Offboarding Confirmation
Close the loop with a final check. Confirm the user has no active logins, no open sessions, and no leftover roles.
Run a scan for accounts tied to their email, username, or employee ID. Check cloud keys, shared drives, and license seats one last time.
You should also ask the manager to confirm data handoff and device return status.
Only close the offboarding ticket when every task is done. Then, mark the user as fully offboarded in your systems to keep records clean and organized.
Common JML Lifecycle Challenges (and How to Fix Them)
Even with clear joiner, mover, and leaver steps, you may still encounter challenges. Here are the most common difficulties to expect and tips on how to resolve them.
Disconnected Systems
Many IT teams run HR, IAM, SSO, and MFA in separate tools that don’t share updates. That leads to late onboarding, missed transfers, and slow offboarding.
Avoid these consequences by using your HR software as the source of truth for employee information and JML lifecycle updates.
Then, connect HRIS to your directory service (Active Directory, Entra ID, Okta) to ensure real-time updates and avoid delays.
Manual Processes
When IT teams handle JML tasks by hand, the work piles up fast. Errors also increase because different people follow varying rules or steps.
Use a structured checklist to manage user access consistently throughout their tenure within your company. Set up automated workflows that reduce manual workload and improve operational efficiency.
Consider using onboarding and offboarding software to streamline provisioning and deprovisioning tasks.
Poor Communication Between HR and IT Teams
If HR employees log access changes late or managers do not report them, IT departments can’t act in a timely manner.
Fix this with a shared JML policy that says who reports changes, how fast, and in what system. Add required HR fields like start date, role change date, and end date.
Then, set up automated alerts so IT and security teams get the update as soon as HR saves it.
Privilege Creep
Over time, people retain access to old roles and past projects. This is common after internal transfers.
To avoid privilege creep, automate deprovisioning during every move so that access is removed right away, not weeks later. Keep exceptions rare. Set an end date for any short-term access.
You should also conduct regular access reviews for all connected systems to keep permissions updated.
Compliance Violations
Audits fail when access records are missing, approvals aren’t saved, or leavers still have active logins. You end up paying expensive non-compliance fines or legal fees.
To achieve and maintain regulatory compliance, save every JML action in one record. Store approvals in that same system. Then, keep offboarding reports so you can prove access was removed at the right time.
Automate the JML Lifecycle Process With ezOnboard
ezOnboard by CloudView Partners automates joiner, mover, and leaver steps by integrating your HR systems with Active Directory (Entra ID).

Once fully integrated, ezOnboard instantly reflects your approved HR changes in AD. That means new hires gain access to the necessary tools on day one, while departing employees are automatically removed from company systems.
The platform also tracks role changes within the organization. It immediately updates access rights to prevent privilege creep and meet data protection regulations.
ezOnboard helps you save time, avoid errors, and provide positive employee experiences. Your IT team stops chasing tickets and can focus on projects that matter.
Request a demo today to see ezOnboard in action! You can also check this ROI calculator to learn how much money you can save.
FAQs About the JML Lifecycle
What is the JML process flow?
The JML process flow is the set of steps you follow to manage access for joiners, movers, and leavers. IT teams take care of provisioning, update old permissions when roles change, and remove all access during offboarding.
What does JML stand for?
JML stands for joiner, mover, and leaver. These describe the main points when a worker’s access needs to change. A joiner is a new hire, a mover is someone who changes roles, and a leaver is someone who exits the company.
What is the meaning of JML?
JML means the entire lifecycle of an individual within your company. It guides how IT handles access from day one, through any role changes, and until the last day. The goal is to match access to the user’s current job and revoke access when that job changes or ends.
What is JML in HR?
In HR, JML involves tracking user changes across hiring, role moves, and exits. Human resources staff can record these changes in the HR system, which acts as the source of truth for identity information.

See Your Cost Savings With EzOnboard
See how much you can save on IT onboarding and offboarding with ezOnboard

Call
(732) 755-0805
info@cloudviewpartners.com
ezonboard@sanjaym.sg-host.com